OUTBOUND ONLY
Node initiates connections
SECURITY BY ARCHITECTURE
Tally and Prism Node stay inside your environment. Node initiates encrypted outbound communication with Prism Cloud, so no inbound firewall rule or publicly exposed Tally port is required.
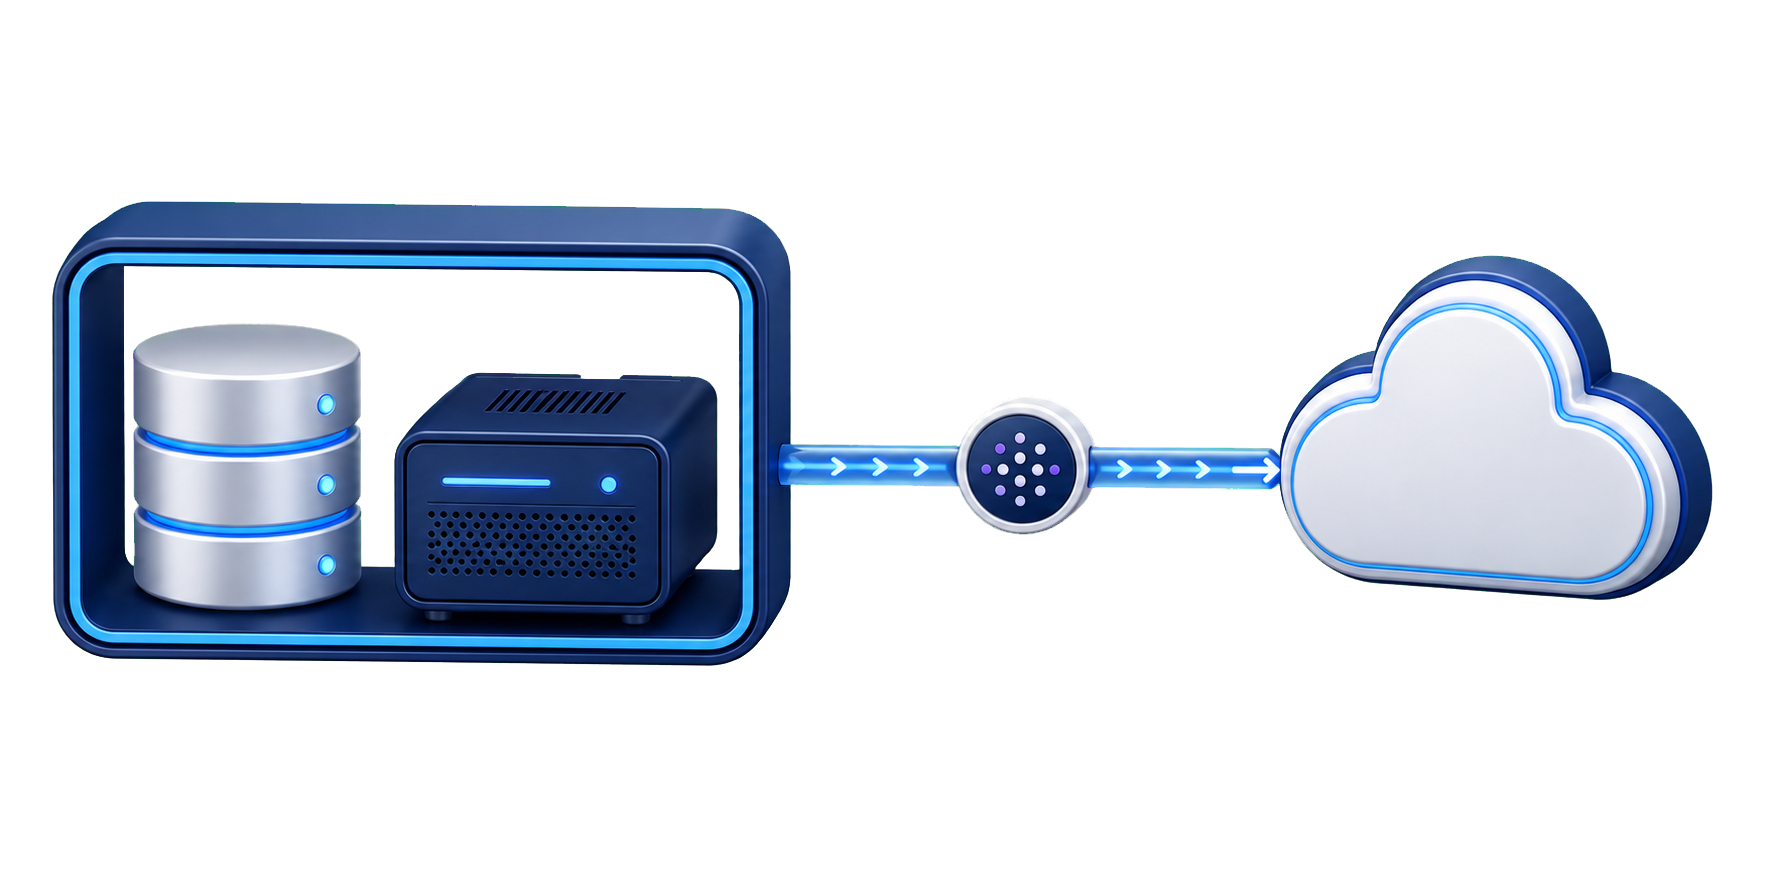
Node initiates connections
Tally stays behind the firewall
HTTPS internet traffic
Access checked centrally
Customer boundaries enforced
DATA BOUNDARY
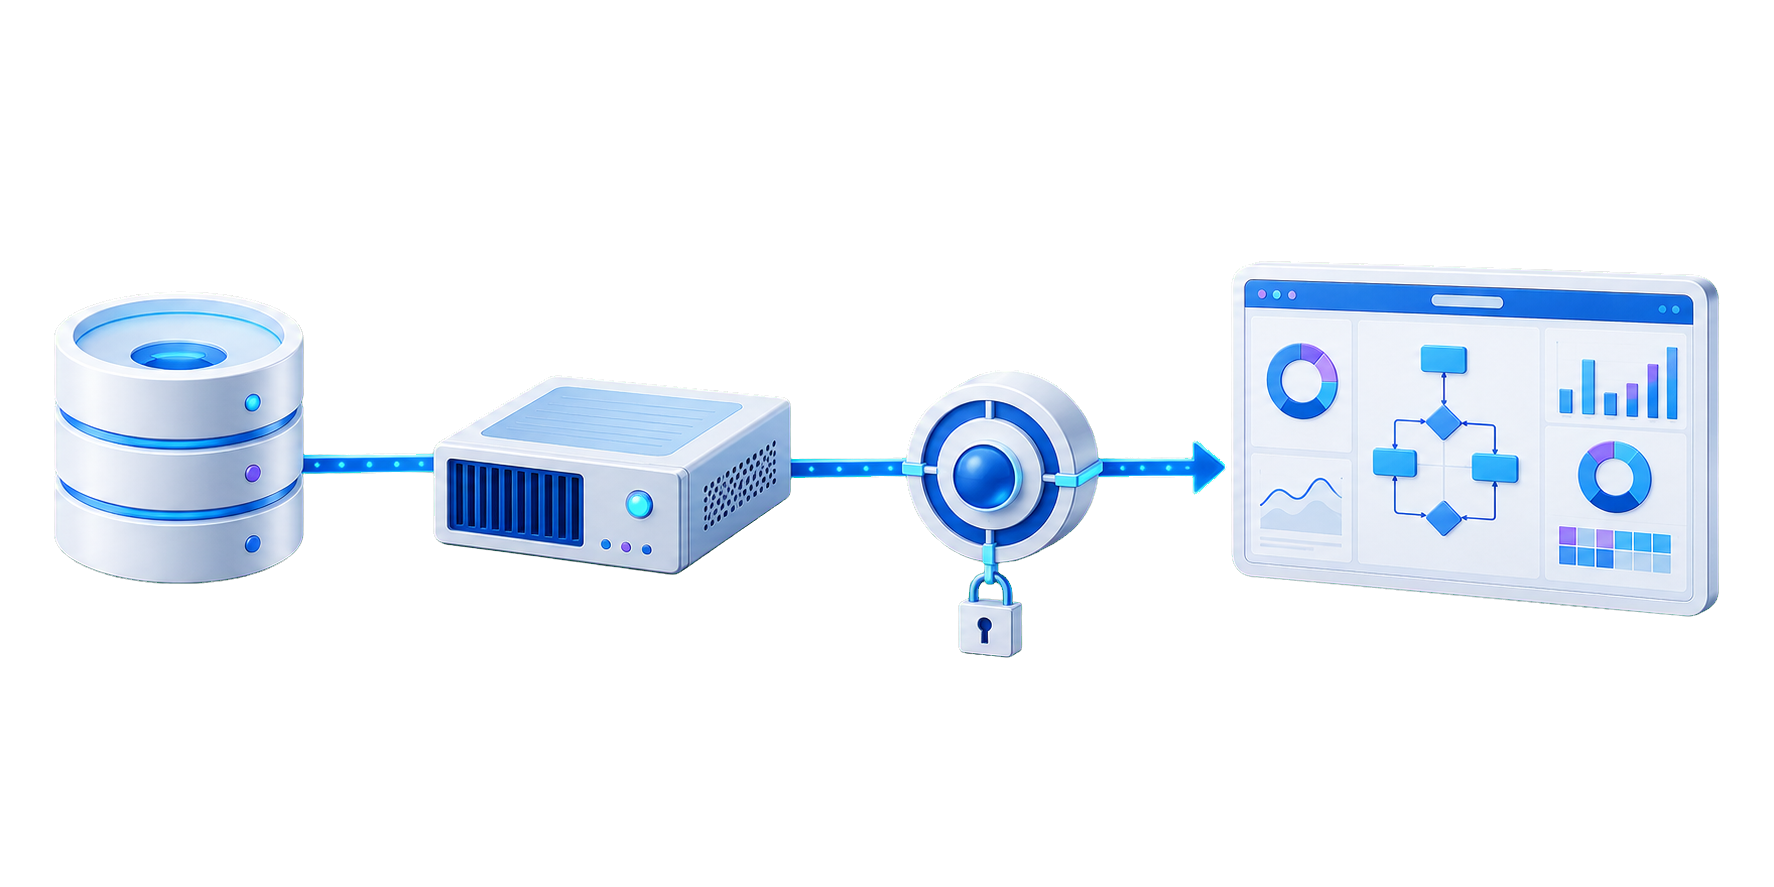
Prism extends Tally through a controlled working copy of relevant operational data—not by opening Tally to the internet.
Tally company data and Prism Node
Relevant operational data
Workflow states, approvals and operational records
Approved transactions, status and references
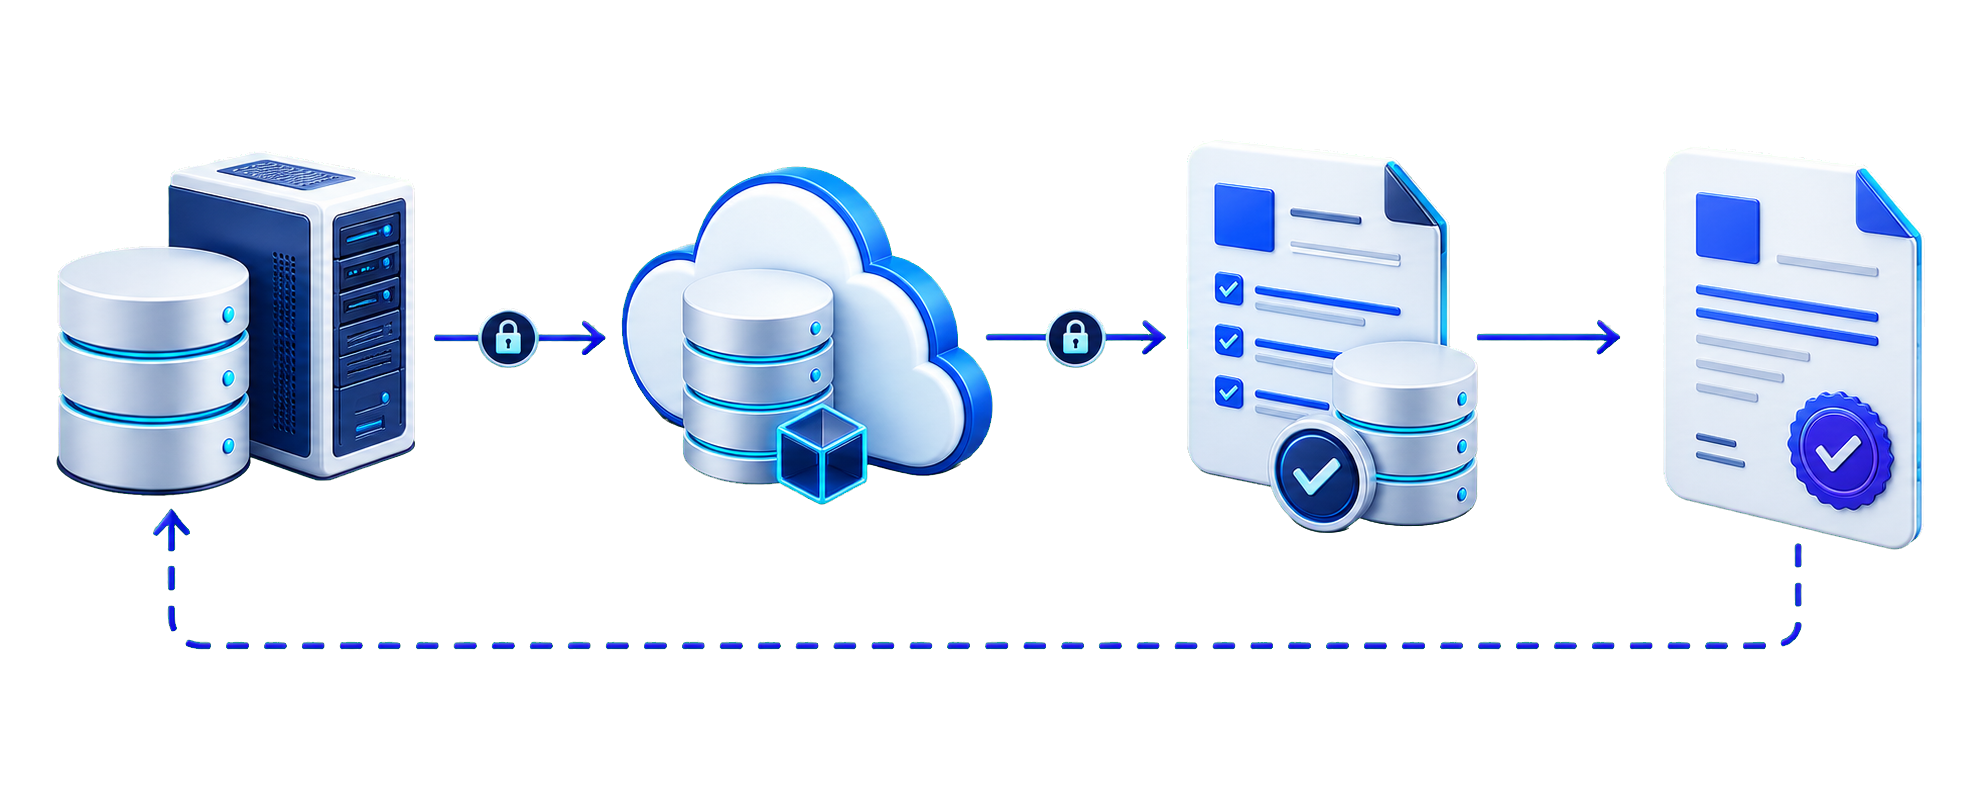
Tally company data and Prism Node
Relevant operational data
Workflow states, approvals and operational records
Approved transactions, status and references
Tally remains the system of record.
ACCESS ENFORCEMENT
Signing in is only the start. Prism verifies the user, authorises the requested action and applies the correct customer, company and warehouse scope before data is returned.
Is the user signed in?
Can this action be performed?
Which records apply?
Allowed data only
Is the user signed in?
Can this action be performed?
Which records apply?
Allowed data only
ALLOWEDRequest continuesOPERATIONAL FOUNDATIONS
Prism protects credentials and traffic, separates environments and data scope, and governs production change with traceable operational evidence.
Credentials kept out of application code.
Internet communications use HTTPS.
DEV, QA and LIVE remain isolated.
Customer, company and warehouse boundaries are enforced.
Production change follows controlled promotion.
Events and references support investigation.
CONNECTIVITY RESILIENCE
When a connection is interrupted, Prism queues pending exchanges, retries in a controlled sequence and checks for duplicate submissions before confirmation.
Exchange queued locally
Retry in controlled sequence
Check for duplicate submission
Send to Prism successfully
Exchange confirmed
Exchange queued locally
Retry in controlled sequence
Check for duplicate submission
Send to Prism successfully
Exchange confirmed
Scoped to temporary connectivity interruption—not backup or disaster recovery.
SHARED RESPONSIBILITY
Prism protects the cloud service and controlled exchange. You remain in control of the environment, accounts and devices around Tally.
Prism application services run in Google Cloud europe-west1.
PRACTICAL QUESTIONS
Clear architecture deserves clear explanations.
No. Tally and Prism Node stay within the customer environment. Prism Node initiates encrypted outbound communication with Prism Cloud; Prism Cloud does not initiate an inbound connection to Tally.
Relevant operational data needed by the enabled Prism workflows is synchronised to Prism Cloud as a controlled working copy. Prism also holds Prism-native workflow states, approvals and operational records. Tally remains the system of record for the Tally data it holds.
No inbound firewall rule or publicly exposed Tally port is required for Prism Cloud. Prism Node initiates the outbound exchange using HTTPS. Your local network and endpoint controls remain under your control.
Prism checks that the user is signed in, verifies that the requested action is authorised and applies the relevant customer, company and warehouse scope before returning data.
Data scope is enforced server-side. Each request is limited to the customer, company and warehouse context that applies to the authorised action.
Prism Node can queue pending exchanges, retry them in a controlled sequence and check for duplicate submissions before confirmation. This is connectivity resilience; it is not a backup or disaster-recovery commitment.
Prism application services run in Google Cloud's europe-west1 region.
You remain responsible for Tally configuration, authorised users, the Prism Node host and network, physical access, user onboarding and removal, passwords, devices, local Tally backup and recovery, endpoints and firewall management.
EXTEND TALLY WITH CONFIDENCE
Prism creates a controlled route from Tally to the operational workflows your teams need—without exposing Tally to the internet.
Book a demo